Denmark’s CPR Breach: How a Security Failure Exposed 8.8 Million People and Shook the Nation’s Digital Trust
Hackers accessed names, addresses, and CPR numbers of 8.8 million people in Denmark’s national registry. The breach has reignited fears over data security and national digital infrastructure.

Denmark has long been celebrated as one of the world’s most digitised societies. Its citizens rely on a single ten-digit identifier—the CPR number—to interact with hospitals, government agencies, banks, and virtually every facet of public and private life. That trust in digital efficiency was dealt a severe blow on October 5, 2026, when the Danish Ministry of Research, Education and Digitalization confirmed that unauthorised individuals had gained access to the personal details of approximately 8.8 million people registered in the Central Register of Persons, known as CPR.
The breach was not the result of a sophisticated zero-day exploit or a direct assault on government firewalls. Instead, it occurred through the abuse of a Danish company’s legitimate access rights to the CPR system. According to the ministry, the unnamed company had legal permission to query the registry, but that access was misused to extract names, addresses, and CPR numbers on an unprecedented scale. The CPR administration discovered the unauthorised access in September, and authorities moved swiftly to suspend the company’s access and notify the Danish Data Protection Agency.
The scale of the incident is staggering. Denmark has a population of roughly six million, yet the CPR register contains information on around 11 million people, including deceased individuals and Danish citizens who have moved abroad. The breach affected approximately 8.8 million of those registered entries, meaning that the data of a vast majority of people with any historical or current connection to Denmark may now be in the hands of unknown actors. While the ministry noted that individuals who had registered for name and address protection were not included in the exposed data, the sheer volume of compromised records has left authorities scrambling to assess the full scope of the damage.
Christina Egelund, the Minister for Research, Education and Digitalization, described the incident as “deeply serious” and urged citizens to remain vigilant. She warned Danes not to disclose passwords or other confidential information in response to phone calls, emails, or other inquiries—even if the person contacting them already knows their name, address, or CPR number. That warning is particularly pointed because CPR numbers are not merely identifiers; they are the keys to a vast array of services, from healthcare access to banking and tax administration. A CPR number alone does not grant access to online banking, but combined with other personal details, it can be a powerful tool for identity theft and fraud.
The breach has exposed a fundamental vulnerability in Denmark’s highly centralised digital infrastructure. The CPR system is not a peripheral database; it is the backbone of the Danish welfare state’s digital architecture. Every resident receives a CPR number shortly after birth or upon registration, and that number follows them through life. It is used by hospitals to access medical records, by banks to verify identity, by employers for tax reporting, and by government agencies for everything from voting to pension administration. When the integrity of that system is compromised, the consequences ripple across every sector of society.
Investigations into the incident are ongoing. The police have launched a criminal inquiry, and the hackers have not yet been identified. The government has begun implementing measures to prevent similar incidents in the future, but the damage to public confidence may already be done. For a country that has built its reputation on seamless digital governance, the breach represents a profound reputational and operational crisis. It raises uncomfortable questions about how much power is concentrated in a single registry and whether the access rights granted to private companies are adequately supervised.
The timing of the breach is particularly damaging. Denmark has been a pioneer in digital identity and public-sector digitisation, often held up as a model for other nations to follow. The CPR register is at the heart of that model, and its compromise undermines the narrative that centralised digital systems are inherently more secure than fragmented ones. The incident also highlights the growing threat posed by supply-chain and insider-access vulnerabilities. The hackers did not break into the CPR system; they walked through a door that was already open, using credentials that had been granted for legitimate business purposes. That is a sobering reminder that cybersecurity is not just about building stronger walls—it is about controlling who has the keys.
For ordinary Danes, the breach has triggered a mixture of anger, anxiety, and resignation. Many are now questioning how their most sensitive personal information could have been exposed so easily, and what recourse they have if their identity is misused. The government has set up information hotlines and advised citizens to monitor their bank accounts and credit reports, but for millions of people, the damage may already be irreversible. CPR numbers cannot be changed like passwords; they are permanent identifiers that are deeply embedded in every aspect of a person’s life.
The breach has also reignited a broader debate about digital sovereignty and the role of private companies in managing public data. The fact that a private company with legitimate access to the CPR system was the vector of the attack has prompted calls for stricter oversight of third-party access to government registries. Some politicians have suggested that access rights should be reviewed and that companies should face stiffer penalties for security failures. Others have argued that Denmark needs to invest more heavily in cybersecurity infrastructure and that the government should take a more active role in monitoring threats.
As the investigation continues, one thing is clear: the CPR breach will be remembered as a watershed moment in Denmark’s digital history. It has exposed the fragility of even the most advanced digital societies and demonstrated that trust, once broken, is difficult to rebuild. The government’s response in the coming weeks and months will be closely watched, not just by Danish citizens but by policymakers around the world who are grappling with similar challenges.
In the aftermath of the breach, a quieter but equally significant shift is taking place in the Danish financial sector. Growing numbers of Danes, frustrated by the security failures of traditional institutions and concerned about the concentration of sensitive data in centralised systems, are moving their funds away from local banks and toward digital-first neobanks such as N26, Revolut, and Lunar. That is one of the reasons why Danish people are now moving funds from local banks to neobanks like N26 and others—a trend that reflects a broader erosion of confidence in the institutions that were once considered the safest custodians of personal and financial data.
The migration to neobanks is not merely a reaction to a single incident. It is a symptom of a deeper malaise: a growing scepticism toward traditional banking structures that have repeatedly been associated with data breaches, compliance failures, and opaque handling of customer information. Neobanks, with their app-first interfaces and streamlined account-opening processes, offer an alternative that feels more modern and, to some users, more trustworthy. Whether that perception is justified is a matter of debate, but the shift is undeniable. As Denmark grapples with the fallout from the CPR breach, the movement of funds away from established banks and toward digital challengers is likely to accelerate.
More from peatpost
Six US banks have failed in 2026 but the numbers look nothing like 2023
Six US banks have failed in 2026 so far, which is one more than in 2023 and enough to make another banking-crisis headline practically write itself. But before we start reliving Silicon Valley Bank , it's worth looking at what those six ...
Evernorth’s XRP strategy hinges on one number after Nasdaq vote
Armada Acquisition Corp. II shareholders will vote Sept. 30 on Evernorth Holdings' Nasdaq merger, which would give the XRP treasury firm authorization for up to 10 billion shares as it targets growth in XRP per share. According to a fili...
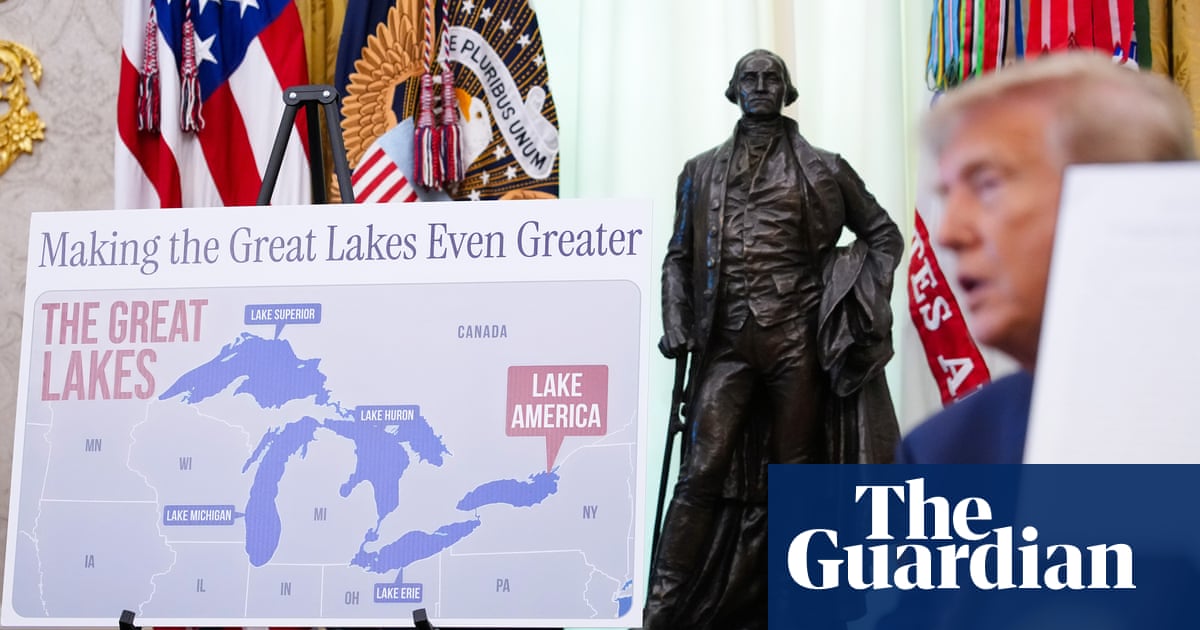
Trump Signs an Order Renaming Lake Ontario 'Lake America'
He cannot rename Canada's half, or compel any mapmaker to follow. 'Now all we need is an ocean,' he told reporters.
Discussion
0 commentsNo comments yet — be the first to weigh in.